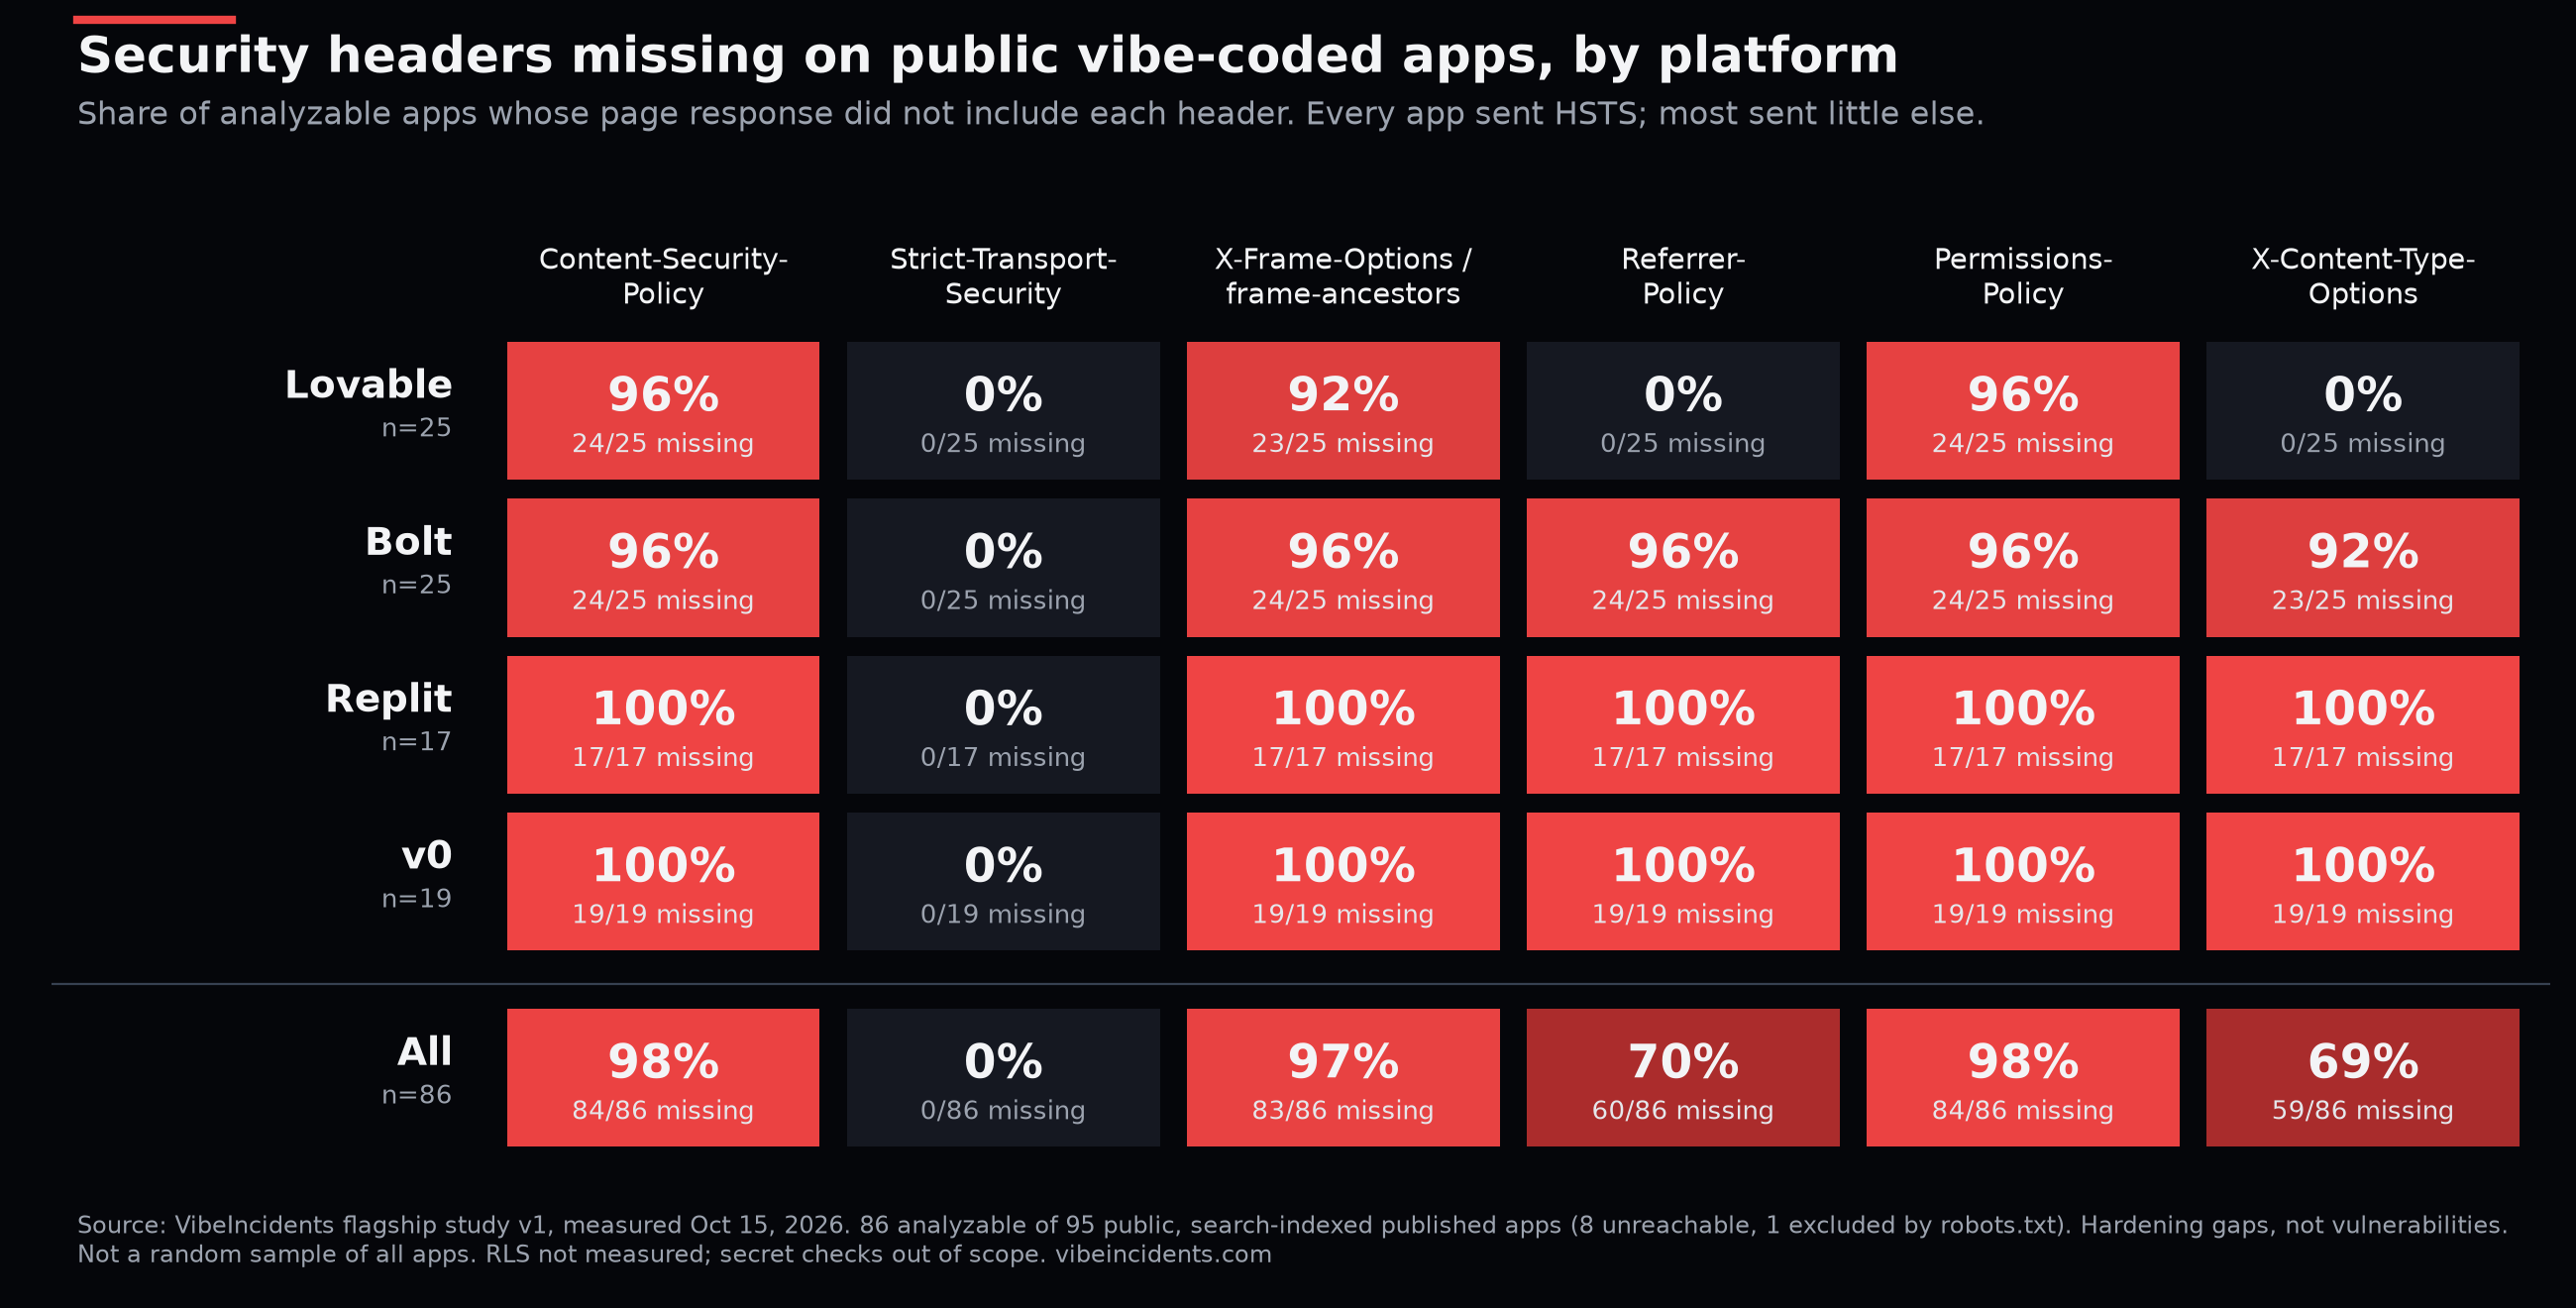
Free-to-use chart: security headers on vibe-coded apps
You can republish this chart and its data anywhere, including commercially. Please keep the credit line and the link back to VibeIncidents.
| Missing CSP | Missing HSTS | Missing X-Frame-Options / frame-ancestors | Missing Referrer-Policy | Missing Permissions-Policy | Missing X-Content-Type-Options | |
|---|---|---|---|---|---|---|
| Lovable (n=25) | 24 (96%) | 0 (0%) | 23 (92%) | 0 (0%) | 24 (96%) | 0 (0%) |
| Bolt (n=25) | 24 (96%) | 0 (0%) | 24 (96%) | 24 (96%) | 24 (96%) | 23 (92%) |
| Replit (n=17) | 17 (100%) | 0 (0%) | 17 (100%) | 17 (100%) | 17 (100%) | 17 (100%) |
| v0 (n=19) | 19 (100%) | 0 (0%) | 19 (100%) | 19 (100%) | 19 (100%) | 19 (100%) |
| All (n=86) | 84 (98%) | 0 (0%) | 83 (97%) | 60 (70%) | 84 (98%) | 59 (69%) |
Data: VibeIncidents research, security headers on 86 public vibe-coded apps, measured Oct 15, 2026. Public, search-indexed published apps, not a random sample. 8 of 95 apps were unreachable and 1 was excluded because its robots.txt disallowed our crawler; all 9 are left out. A missing header is a hardening gap, not a breach.
Embed the live chart
Or use the image